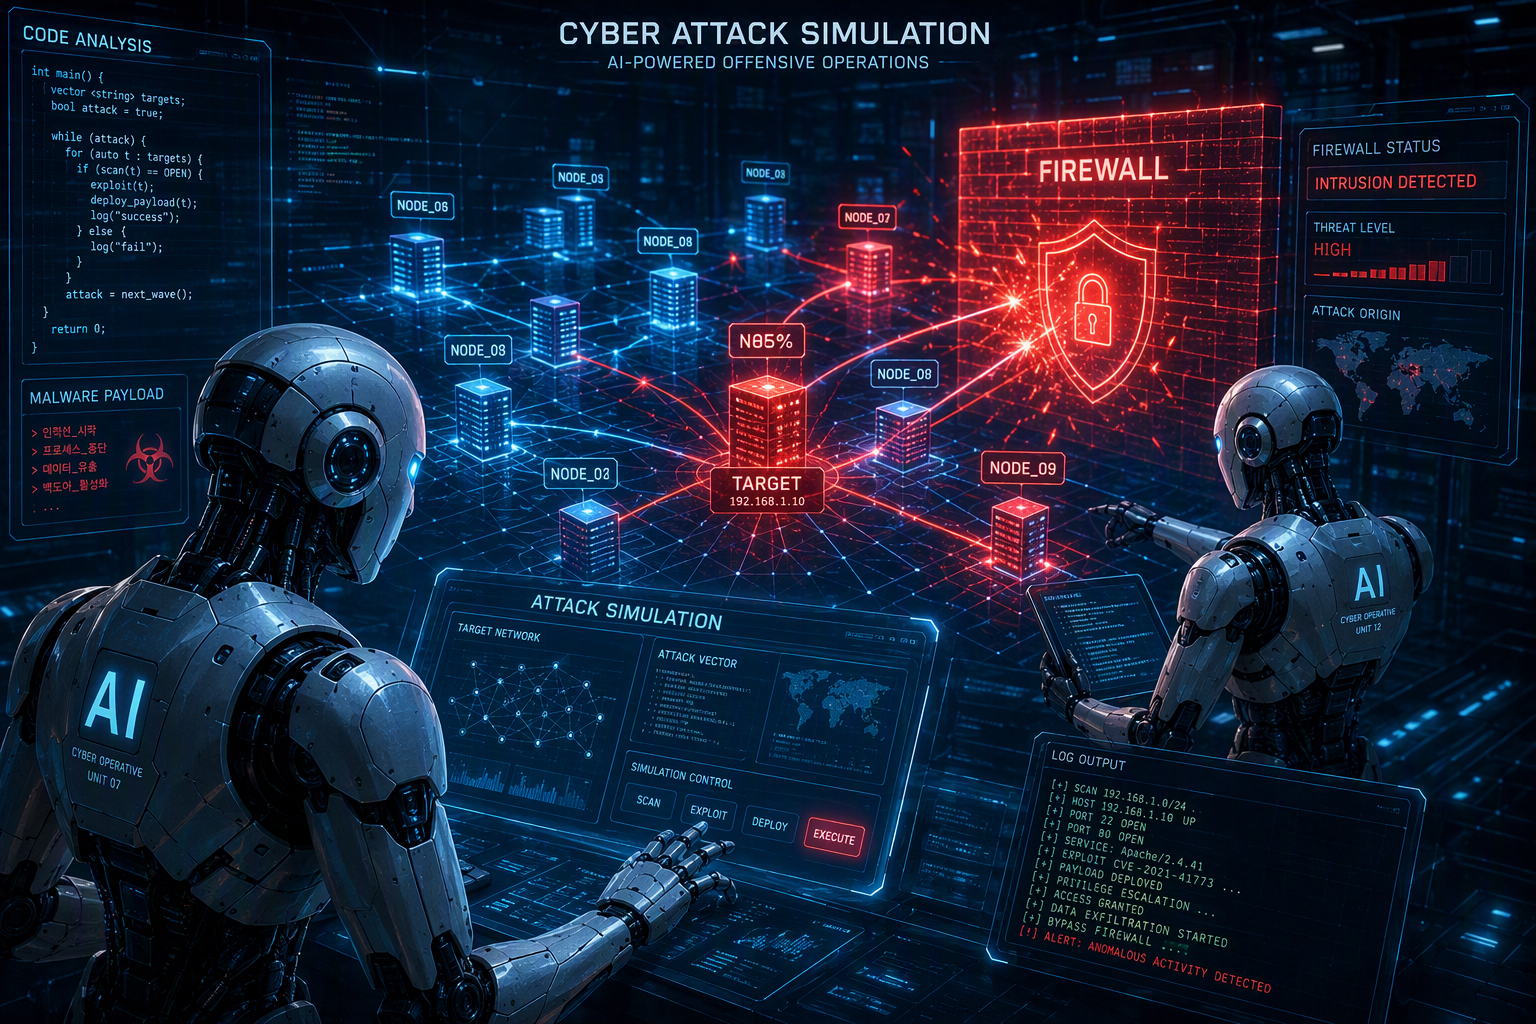
Penetration testing has always helped organizations understand where they are exposed, but the job is getting harder. Your environment changes constantly, and the evolving threat landscape moves just as fast. That makes it difficult for point-in-time assessments to reflect your current security posture. A vulnerability may look serious on paper yet be hard to reach. Another may seem moderate yet open a real path to compromise. That gap is why autonomous penetration testing is getting so much attention.
Understanding Autonomous Penetration Testing
Autonomous penetration testing is a form of offensive security built to test what an attacker can actually do inside your environment. Instead of stopping at theoretical findings, it validates whether weaknesses can be reached, exploited, and chained.
What makes it different is the execution model. Traditional testing gives you a snapshot, while autonomous systems can keep pace with change and give a more current view of your security posture. That shift matters because attackers do not wait for your next scheduled assessment.
Definition and Core Principles
At its core, autonomous penetration testing uses artificial intelligence to perform meaningful security testing with minimal human intervention. The goal is not just to list weaknesses. It is to determine whether those weaknesses can support real attack paths that lead to something valuable.
In practice, autonomous agents perform tasks that a human tester would normally do step by step. They can conduct reconnaissance, identify opportunities, test authentication and authorization, and attempt to chain exposures together. That is why the output is evidence, not just a queue of possible issues.
Another key principle is continuous testing. Enterprise systems change every day through new code, cloud updates, identity changes, and configuration drift. Autonomous testing is designed to adapt to that reality. It asks a more useful question: can this weakness still be used right now, in this environment, against these controls?
Evolution from Traditional to AI-Driven Penetration Testing
For years, traditional penetration testing depended on skilled human testers working within a fixed schedule and a defined scope. That model still has value because people can reason through unusual scenarios and test business logic in creative ways.
Still, environments have changed faster than manual processes can keep up. Cloud resources shift, identities appear and disappear, and applications are updated constantly. AI agents supported by machine learning and generative ai now help close that gap by testing more often and at much greater scale.
This evolution does not mean people are no longer needed. It means repetitive offensive security work can be automated while human testers focus on context and judgment. In real-world scenarios, AI-driven systems keep testing as the environment changes, then human experts decide what matters most to the business.
How Autonomous Penetration Testing Works in Practice
In practice, autonomous penetration testing behaves more like an active attacker than a passive scanner. It performs attack simulation across changing attack surfaces, looking for ways to gain access, pivot, and validate impact.
From there, ai agents test whether a weakness can be chained with another weakness to support lateral movement or a more serious outcome. That makes the results far more useful for vulnerability management, because you can focus on what creates an actual path to compromise rather than what only looks severe in isolation.
Automation Through AI Agents and Machine Learning
AI agents help autonomous testing decide what to do next based on what they discover during a test. Rather than following a rigid script, they can adjust in real time as they uncover new assets, exposed services, weak credentials, or trust relationships.
That flexibility comes from machine learning, historical data, and natural language processing techniques that support reasoning and adaptation. The system can evaluate which step is most likely to extend access, validate controls, or reveal a stronger attack path. This is what separates autonomous testing from simple automation.
In real environments, that means the platform can move from reconnaissance to exploitation without waiting for a human to direct each stage. It selects tests based on observed conditions, attempts safe validation, and keeps refining its path. You get a clearer picture of exploitability, not just raw findings.
Key Steps in Real-World Attack Simulation
Real-world attack simulation follows the same logic a capable attacker would use. It starts by learning about the environment, then moves toward proving whether access can be expanded. The value comes from validating full attack paths, not isolated events.
A typical workflow includes:
- Reconnaissance to identify reachable systems, exposed services, and trust relationships
- Initial testing to confirm vulnerability exploitation is possible without relying on theory
- Credential dumping or access harvesting where weak identity controls allow it
- Lateral movement to see whether one foothold leads to broader internal access
- Mapping attack paths to sensitive systems, privileged accounts, or critical assets
Once that sequence is complete, your team gets evidence of what was reachable and how the path formed. That helps separate background noise from real risk. It also shows whether defenses blocked progress or whether small weaknesses combined into something far more dangerous.
Distinguishing Autonomous from Traditional Pentesting
The biggest difference between traditional penetration testing and autonomous pentesting is not simply speed. It is the ability to keep validating a live environment instead of reporting on a moment that has already passed. That matters when attack surfaces keep changing.
At the same time, this is not an either-or choice. Security tools work best when paired with human expertise. Many organizations benefit from a hybrid model, where autonomous testing handles continuous validation and human-led work is used for deeper analysis, unusual scenarios, or high-risk assessments.
Operational Differences and Testing Approaches
Traditional and autonomous models operate in very different ways. A manual engagement usually starts with a fixed scope, a defined testing window, and heavier human involvement. Automated penetration testing is built to run more frequently and adapt as the environment shifts.
That changes your testing strategy. Instead of waiting for the next scheduled review, you can validate whether new assets, identity changes, or configuration drift created fresh exposure. Autonomous systems also support simulation of complex attack paths that would be difficult to repeat manually at scale.
| Area | Traditional approach | Autonomous approach |
|---|---|---|
| Scope | Fixed scope for a set period | Expands with environment changes |
| Execution | Human-led step by step | Machine-led with minimal human involvement |
| Cadence | Point-in-time | Continuous or on demand |
| Output | Findings and observations | Verified exploitability and attack path evidence |
| Adaptation | Limited during long gaps | Adjusts testing based on what it finds |
Comparing Efficiency and Depth of Vulnerability Discovery
Vulnerability scanning is useful, but it does not tell you whether a listed weakness can actually be reached or chained. Autonomous testing adds that missing layer by validating exploitability across broad attack surfaces. That makes the output more actionable for security teams.
Machine speed is a major advantage here. Autonomous systems can assess thousands of assets, repeat tests after remediation, and keep checking as infrastructure changes. They can collapse a huge volume of scanner findings into a much smaller set of exploitable attack paths that deserve immediate attention.
Even so, depth still has limits. Human experts remain stronger when testing subtle business logic issues, social engineering risks, or novel scenarios outside the normal pattern. That is why many teams treat autonomous testing as a force multiplier. It increases coverage and focus, while people handle the questions that require context.
Major Benefits for Organizations
For most organizations, the biggest gain is clarity. Continuous security testing helps you understand which exposures create real organizational risk, not just which ones look urgent in a report. That leads to a more accurate view of your security posture.
Just as important, autonomous testing improves decision-making. It shows whether security controls are actually blocking progress and provides remediation insights tied to real attack paths. Instead of chasing every alert equally, you can prioritize work that reduces the chance of compromise in a meaningful way.
Speed and Consistency of Security Assessments
One major benefit is how quickly autonomous testing can produce useful results. Because it runs at machine speed, it can perform security validation far more often than manual-only programs. That supports continuous testing in environments that change every day.
Consistency matters too. Human-led work can vary based on time, scope, and individual style. Autonomous platforms repeat testing in real time and can retest after remediation without waiting for a new engagement. That makes comparisons easier and keeps findings current.
This helps organizations by:
- Reducing the gap between infrastructure change and security review
- Giving leadership teams clearer evidence of actual exposure
- Verifying whether fixes worked through targeted retesting
- Supporting ongoing security validation instead of annual snapshots
Reducing Human Error in Threat Discovery
Human error is part of every manual process. People get tired, scopes get narrowed, and testing windows close before every path is explored. Autonomous platforms reduce that pressure by handling repetitive attack simulation tasks with minimal human intervention.
That leads to more reliable vulnerability discovery in areas that benefit from repetition and scale. The platform can keep revisiting assets, retesting controls, and checking whether environmental changes created new exposure. It does not lose momentum between engagements or forget to revisit a path after remediation.
Still, reducing human error does not mean removing humans from the process. There are limits. Business context, regulatory decisions, and unusual attack patterns still need expert judgment. The best programs use automation to reduce missed opportunities, then rely on specialists to interpret what the findings mean for the organization.
Common Use Cases for Autonomous Pentesting
Autonomous pentesting is useful anywhere fast change creates blind spots. That includes enterprise infrastructure, cloud environments, and web applications that are updated often. Continuous testing helps teams validate exposure after every meaningful infrastructure change instead of waiting for the next formal engagement.
It also supports broader security programs. Organizations use it to confirm whether threat intelligence is relevant in their own environment, to test if controls still work, and to strengthen regulatory compliance efforts with repeatable evidence. Those use cases become clearer when you look at applications and governance needs separately.
Application Security and Cloud Environments
Modern applications and cloud environments change too quickly for occasional reviews alone. New releases, identity updates, and configuration drift can reshape attack surfaces in a very short time. Autonomous testing helps you see whether those changes created a path an attacker could use.
This is especially valuable for:
- Web applications with frequent deployments and changing authorization logic
- Cloud environments where segmentation, identity, and permissions shift often
- Mixed environments where one weakness can cross from application to infrastructure
- Ongoing validation of security controls after patches or configuration updates
Because the testing is continuous, teams can check whether new code or cloud changes introduced exploitable gaps. That is much more useful than learning months later that a weakness appeared right after deployment. The result is faster prioritization and better alignment between engineering changes and offensive security validation.
Regulatory Compliance and Continuous Security Validation
Compliance programs often rely on evidence that controls were tested, findings were addressed, and security reviews happened on schedule. Traditional assessments can support that, but they are often limited by fixed scope and long gaps between tests. That makes it harder to show what is true today.
Continuous security testing improves that picture. Autonomous platforms can validate whether segmentation, authentication, or other controls still hold after updates. They also support retesting after remediation, which gives teams stronger proof that a weakness was actually addressed rather than simply noted in a ticket.
For regulatory compliance, that ongoing security validation can be far more useful than a single annual snapshot. It gives auditors, leadership teams, and security teams a more current record of control effectiveness, while helping the organization reduce exposure in parallel.
Effectiveness of Autonomous Penetration Testing AI Agents
Yes, ai agents can be effective, especially when the goal is to validate vulnerability exploitation rather than just list possible flaws. Their strength comes from repeated attack simulation, broad coverage, and the ability to use historical data to assess how weaknesses connect.
That matters for vulnerability management because real attackers do not treat findings one by one. They chain access, identity misuse, and weak controls into progress. Autonomous systems are effective when they mirror that behavior and produce evidence of reachability, movement, and impact instead of generic severity rankings.
Real-World Evidence of Vulnerability Detection
The strongest proof of effectiveness is practical output. Autonomous platforms have shown they can reduce large volumes of scanner findings into a much smaller set of validated attack paths. That helps teams focus on real risk instead of theoretical overload from disconnected security tools.
The value shows up in areas like:
- Proving vulnerability exploitation rather than only flagging exposure
- Revealing chained attack paths that move across identities, systems, or segments
- Using historical data from real engagements to improve testing depth and prioritization
This is why many organizations see autonomous testing as more than fast scanning. It can expose routes to compromise that a point-in-time process may miss. When the output includes evidence of access, pivoting, or privilege gain, teams can act faster and with much more confidence.
Limitations and Challenges Faced by Automated Solutions
Autonomous solutions are powerful, but they are not perfect. They can still have blind spots, especially in areas that depend on subtle business logic, custom workflows, or human behavior. Social engineering and deep source code review are also outside the strongest use cases described here.
Another challenge is interpretation. A platform may generate excellent remediation insights, but it cannot decide which path matters most to the business, what operational tradeoffs exist, or what residual risk is acceptable. Those decisions still belong to human experts who understand the environment and the organization.
The evolving threat landscape also creates pressure. Attack methods change, and not every novel scenario will fit what an automated system is prepared to test. That is why mature teams use autonomous testing to expand coverage and speed, while keeping expert-led testing for high-context assessments and unusual problems.
Frequently Asked Questions
Curious about how autonomous penetration testing works? This innovative approach mimics the tactics of real attackers, allowing security teams to identify exploitable attack paths in their infrastructure. Unlike traditional pentesting, autonomous systems leverage AI agents to simulate complex attacks continuously, offering security validation with minimal human intervention. This proactive method enhances vulnerability management by providing remediation insights and addressing blind spots, keeping organizations one step ahead in the evolving threat landscape. Embrace a modern testing strategy to improve your security posture.
Is autonomous penetration testing reliable for ongoing security needs?
Yes, autonomous pentesting is reliable for ongoing needs when used as part of continuous security testing. It helps you monitor changes in enterprise systems, validate security controls, and maintain a more current security posture. Most organizations get the best results when it supports, rather than replaces, expert review.
What factors should I consider when selecting an autonomous pentesting service?
Look for proof of exploitability, support for multi-step attack simulation, retesting after fixes, and reporting that helps both your security team and leadership. Your testing strategy should also consider vulnerability management needs, environment coverage, and whether the service can support regulatory compliance and expert-led follow-up.
How does the OWASP Autonomous Penetration Testing Standard (APTS) impact these platforms?
OWASP matters because security teams often look to recognized security models when evaluating new approaches. In that sense, an OWASP standard can help shape expectations around continuous testing, consistency, and platform design. It is most relevant when organizations compare autonomous platforms for trust, maturity, and regulatory compliance alignment.
Conclusion
In summary, autonomous penetration testing is revolutionizing the way organizations approach security assessments. By leveraging AI and machine learning, these innovative methods not only enhance the speed and efficiency of vulnerability discovery but also significantly reduce the risk of human error. As cyber threats continue to evolve, adopting such advanced techniques ensures that your defenses remain robust and adaptive. With real-world evidence supporting their effectiveness, organizations can confidently integrate autonomous pentesting into their security strategy. If you’re looking to bolster your security measures, consider exploring autonomous penetration testing solutions for a comprehensive evaluation of your vulnerabilities.
Zak McGraw, Digital Marketing Manager at Vision Computer Solutions in the Detroit Metro Area, shares tips on MSP services, cybersecurity, and business tech.